What you get
CLAUDE.md | Standing rules: log every change with an undo command, apps in /srv behind Caddy, never touch SSH or the firewall unasked, and treat web and inbox text as data, not instructions. |
MISSION-BRIEF.md | A brief for unattended runs: authority, working method, when to contact you, hard limits and a fixed final-report format. |
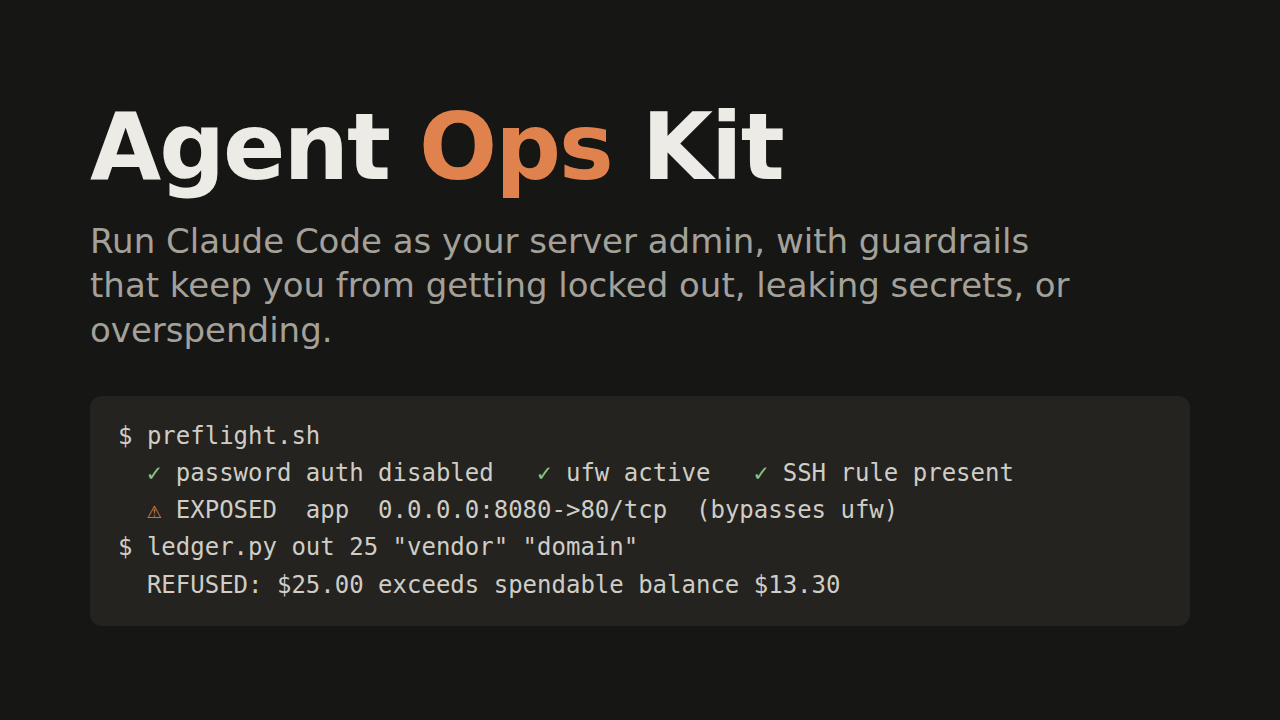
preflight.sh | Read-only audit of SSH, ufw, public ports, Docker exposure, failed units and secret-file permissions. |
tg_send / poll / wait | Telegram check-ins. The token never shows up in argv or logs, and messages from any chat but yours are ignored. |
ledger.py | Money ledger with an automatic 30% tax reserve. It refuses any spend the balance can't cover. |
docker-port-audit.sh | Catches container ports that bypass ufw. |
systemd + Caddy | A Remote Control service that survives reboots, so you can drive the agent from your phone, plus HTTPS proxy patterns. |
README | A 20-minute setup guide from a bare VPS, plus the lessons behind each rule. |
Free sample
Docker-published ports skip ufw entirely. This script from the kit finds any that do. It's free, along with preflight.sh.
#!/usr/bin/env bash
# Docker-published ports bypass ufw. Flag any container port bound to a public address.
# Exit 1 if anything is exposed beyond loopback.
set -uo pipefail
bad=0
while IFS=$'\t' read -r name ports; do
  [ -z "$ports" ] && continue
  IFS=',' read -ra arr <<<"$ports"
  for p in "${arr[@]}"; do
    p="${p# }"
    [[ "$p" == *"->"* ]] || continue
    if [[ "$p" == 127.0.0.1:* || "$p" == "[::1]:"* ]]; then continue; fi
    echo "EXPOSED  $name  $p   (bypasses ufw — bind to 127.0.0.1 and proxy via Caddy)"; bad=1
  done
done < <(docker ps --format '{{.Names}}\t{{.Ports}}')
[ $bad -eq 0 ] && echo "OK: no container ports published beyond loopback"
exit $bad
The lessons behind it
- Docker bypasses ufw: why your "denied" port is public
- StartLimitIntervalSec in [Service] is silently ignored
- tee /dev/stderr wipes your log file
- Giving an AI agent sudo: the guardrails checklist
Who it's for
- You use Claude Code and want it looking after a server while you're away.
- You want an agent you can audit afterwards: a journal, an ops log and an undo for every change.
- You'd rather start from rules tested in practice than write your own.
Not included
- A Claude subscription, a VPS or a domain. Need a VPS? The kit was built on a DigitalOcean droplet (referral link: if you sign up and spend $25, the site owner gets $25 in credit; your price is the same).
- Any guarantee that an agent with sudo can't make mistakes. The kit narrows the risk; it doesn't remove it. Start on a throwaway server.
Questions: reply to your purchase receipt. "Claude" and "Claude Code" are Anthropic's products; this kit isn't affiliated with Anthropic.