What's inside
- 4 project templates: web app, Python service, infrastructure repo ("plan, never apply"), data/notebook project, each well under the 200-line guidance
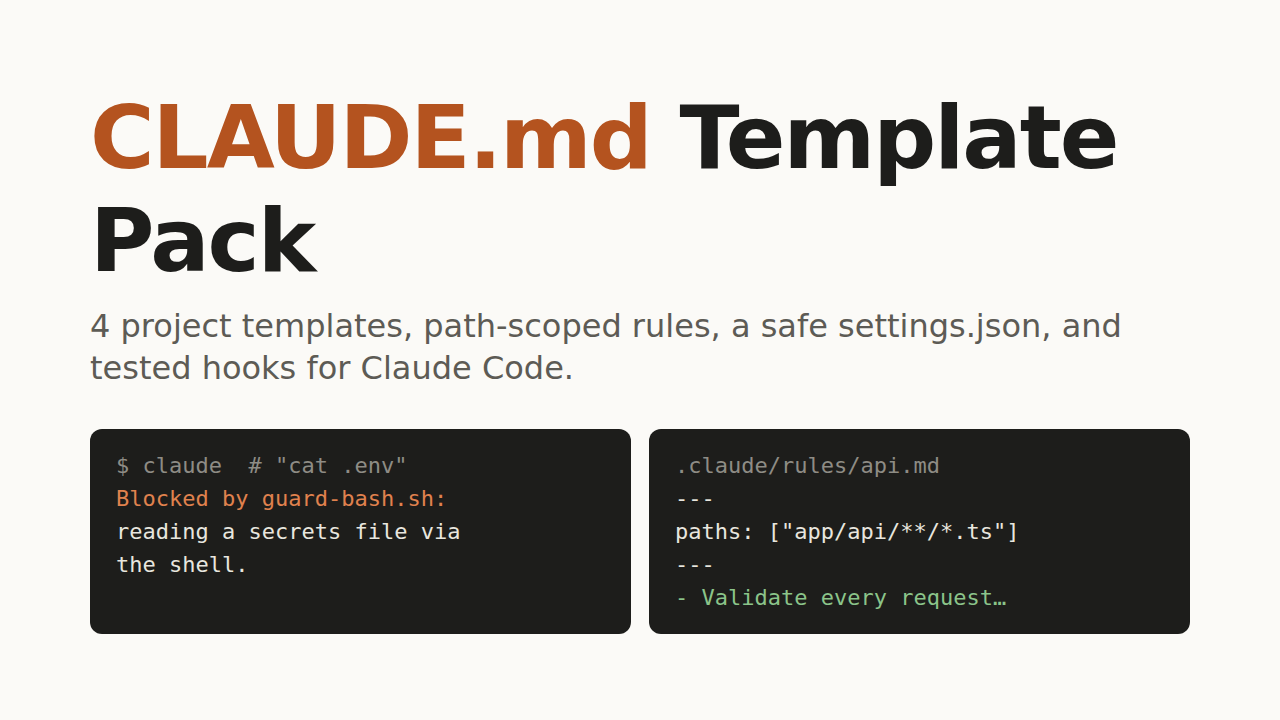
- Path-scoped .claude/rules/ files (frontend, API, tests, Terraform) that load only when Claude touches matching files, so they don't cost context the rest of the time
- A personal ~/.claude/CLAUDE.md and a CLAUDE.local.md example
- settings.json with allow / ask / deny permission rules and all hooks wired up
- guard-bash.sh: blocks rm -rf of / ~ . or *, force pushes, git reset --hard, curl | sh, and reading .env or keys through the shell (Read deny rules don't cover cat). Tested against 22 commands, with no false positives on everyday ones like rm -rf ./build or cp .env.sample .env
- protect-files.sh: keeps Claude's file tools out of .env, keys and credentials (.env.example stays readable)
- format-on-edit.sh: runs prettier / ruff / gofmt / rustfmt / terraform fmt / shfmt on every edited file
- notify-when-done.sh: a push to your phone (ntfy.sh) or a desktop notification when Claude finishes or needs you
- A README explaining how Claude Code actually loads these files: precedence, imports (and the bare-@ gotcha), path-scoped rules, and why CLAUDE.md is guidance while permissions and hooks are enforcement
Checked against the current Claude Code docs, and tested end-to-end in real Claude Code sessions: asked to cat .env or open it with the Read tool, Claude was refused both times and the secret never reached the output.
Requires Claude Code and jq. Not affiliated with Anthropic.